

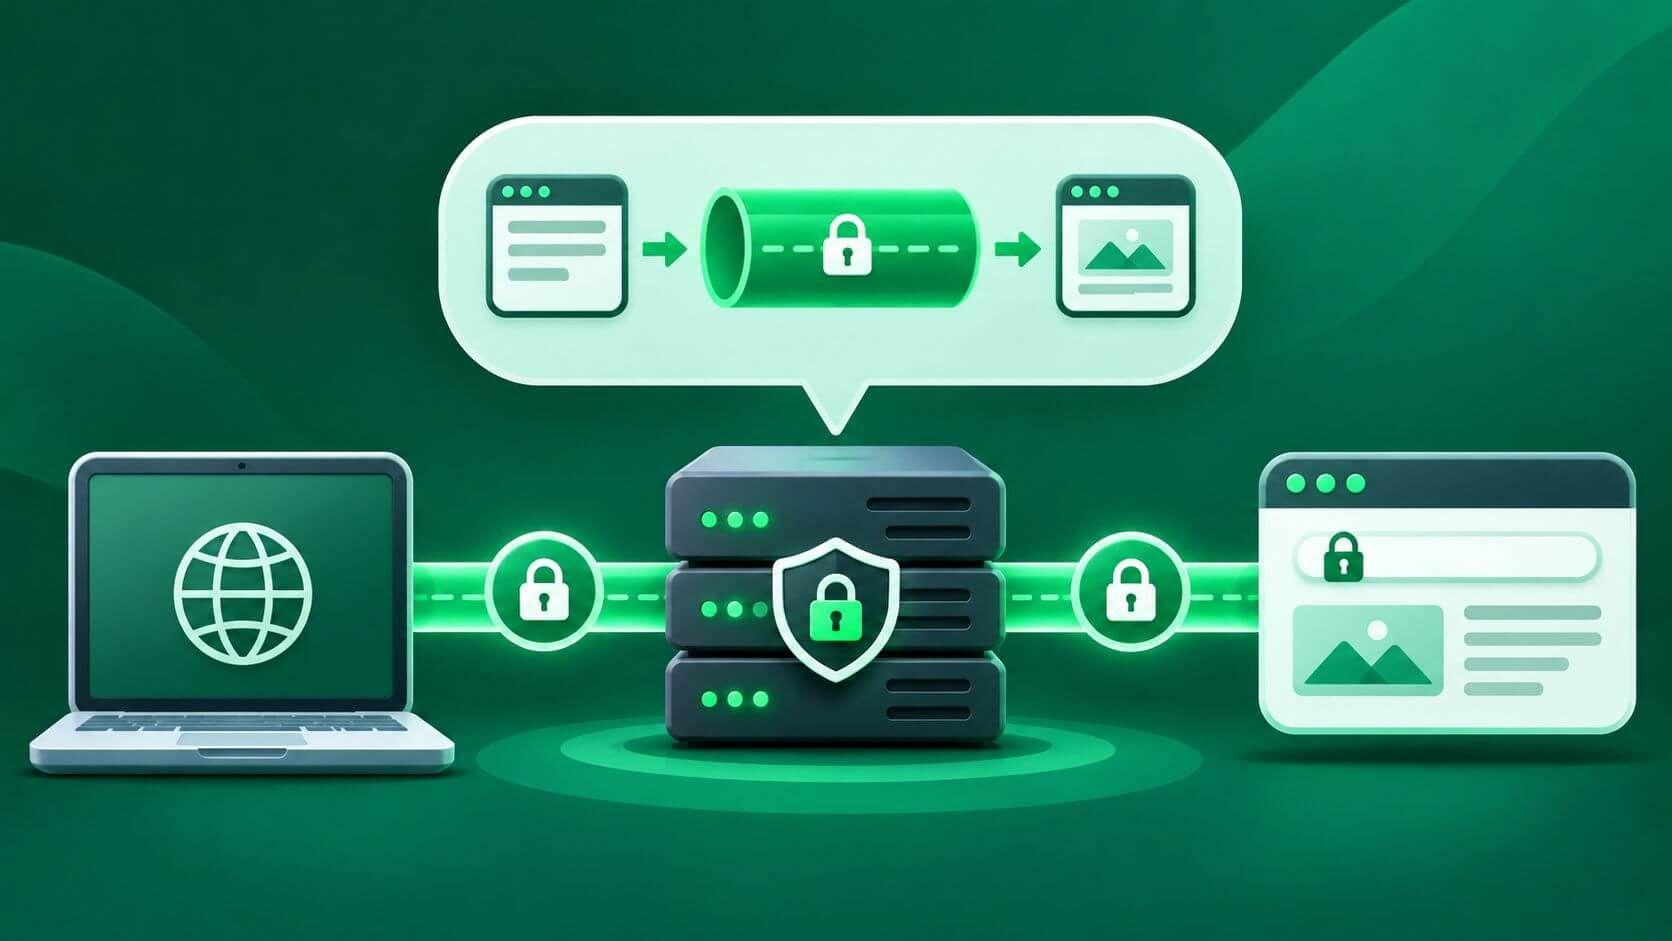
HTTPS proxies are frequently described as proxies that “encrypt web traffic.” That description misses an important distinction: an HTTP proxy can tunnel an encrypted HTTPS connection without encrypting the connection to the proxy itself. An HTTPS proxy, in the stricter protocol sense, uses TLS between the client and the proxy as well.
Understanding that difference helps developers configure crawlers, diagnose TLS handshake failures, and determine which party can observe request metadata. This guide explains HTTP CONNECT, certificate verification, common error codes, and practical tests with cURL and Python.
The term HTTPS proxy is used in two ways:
Both arrangements can access HTTPS websites, but their security properties differ. The scheme in the proxy address (http:// or https://) describes how the client talks to the proxy; the scheme in the destination URL describes the requested resource.
| Connection | Client-to-proxy link | Client-to-website content |
|---|---|---|
http://proxy → https://site |
Plain HTTP for tunnel setup | TLS-encrypted inside CONNECT tunnel |
https://proxy → https://site |
TLS-encrypted proxy connection | Separate TLS session to website inside tunnel |
http://proxy → http://site |
Usually plain HTTP | No destination TLS |
For teams assessing proxy infrastructure, start with the ProxiesThatWork homepage to understand its advertised HTTP proxy capabilities. Verify whether a provider supports HTTPS destinations, TLS to the proxy endpoint, or both; those are not interchangeable promises.
CONNECT is an HTTP method defined by RFC 9110, Section 9.3.6. It tells a proxy to establish a connection to a specified host and port and, if successful, forward data in both directions without interpreting it as ordinary HTTP messages.
For an HTTPS request to example.com, the sequence is:
CONNECT example.com:443 with the required host information and any applicable proxy authorization.2xx response, commonly 200 Connection Established, means the tunnel is active. A 407 means proxy authentication is required or failed.A simplified HTTP/1.1 exchange looks like this:
CONNECT example.com:443 HTTP/1.1
Host: example.com:443

HTTP/1.1 200 Connection Established
After the blank line following the successful response, subsequent bytes belong to the tunnel—not to a new plaintext HTTP response from the proxy. CONNECT itself is not encryption; TLS provides encryption after tunnel establishment.
HTTP/2 also supports CONNECT, but carries the tunnel on a stream rather than converting the entire connection into a tunnel. The basic principle remains the same.
TLS 1.3, specified in RFC 8446, provides authentication, confidentiality, and integrity when correctly implemented and validated. With a conventional HTTP CONNECT proxy, the TLS handshake to the destination takes place between the client and the destination, with the proxy forwarding the bytes.
A non-intercepting proxy therefore cannot ordinarily read HTTPS page bodies, cookies, or application headers carried inside the protected session. It can still observe connection timing, traffic volumes, and the destination host and port requested with CONNECT. On a plaintext client-to-proxy link, intermediaries on that network path may also observe the CONNECT request and any unprotected proxy authentication data.
With an HTTPS proxy endpoint, the outer TLS connection protects client-to-proxy communication against observers along that hop. The proxy itself still receives the destination details needed to route the tunnel. Outer TLS is not a substitute for verifying the destination certificate.
Some enterprise gateways explicitly intercept TLS. Instead of merely relaying encrypted bytes, they terminate the client TLS session and establish another session to the destination. This typically requires the client to trust an organization-managed certificate authority (CA).
That model is fundamentally different from ordinary CONNECT passthrough. It can provide security inspection, but the gateway can also read decrypted content. Use it only under authorized, documented policies, and verify the certificate chain rather than accepting unexpected issuers.
Once the destination TLS handshake begins, the client evaluates the presented certificate and supporting chain. Common checks include:
These checks apply even when the connection traverses several proxies. If the proxy endpoint itself uses HTTPS, two independent certificate-verification steps may occur: one for the proxy and one for the destination.
Certificate failures are not evidence that proxies “do not support HTTPS.” They usually indicate a problem with one TLS endpoint, its trust configuration, or unexpected interception.
| Symptom | Likely layer | First checks |
|---|---|---|
407 Proxy Authentication Required |
Proxy authorization | Approved source IP, credentials, provider policy |
403 or failed CONNECT |
Proxy policy or upstream restriction | Target port, destination, allowed tunnel rules |
502 Bad Gateway |
Proxy/upstream connection | Destination reachability, proxy logs, DNS, network |
SSL certificate problem / cURL error 60 |
TLS certificate verification | Issuer, hostname, expiry, CA bundle, inspection |
SSL connect error / cURL error 35 |
TLS handshake | TLS versions, proxy scheme, server compatibility |
ERR_TUNNEL_CONNECTION_FAILED |
Tunnel setup or proxy connection | Proxy host/port, authentication, CONNECT response |
| Connection timeout | Network path | Firewall, routing, proxy availability, destination |
Error wording varies by application, and an HTTP status is not always produced when TLS fails. A destination 403 after a successful tunnel and TLS handshake differs from a proxy's refusal to create that tunnel.
The destination certificate may be valid but signed by a CA absent from the client's trust store. Confirm the issuer, update an outdated trust bundle, or install a verified, authorized internal CA where TLS inspection is intentionally deployed. Never import an unfamiliar CA simply to make an error disappear.
The URL's hostname must match the certificate identity. Check redirects, server configuration, validity dates, and local clock synchronization. Connecting by IP address to a host configured for name-based TLS can also cause identity mismatches.
Using https://proxy-host:port against a proxy that expects plaintext HTTP may fail before CONNECT is sent. Conversely, using http:// when the endpoint requires TLS produces another protocol mismatch. Confirm the proxy endpoint scheme and port from the provider's specifications.
An enterprise interception gateway can present a certificate signed by a private CA. An origin server can also omit necessary intermediate certificates. Inspect the actual chain presented, distinguish intentional inspection from potential tampering, and fix trust or server configuration at the appropriate layer.
Use a test endpoint you are authorized to access. Replace the placeholder proxy hostname and port with the provider's documented values.
curl -v --proxy http://proxy.example.test:8080 \
  --connect-timeout 5 --max-time 20 \
  https://example.com/ -o /dev/null
Look for CONNECT example.com:443, a successful tunnel response, destination certificate verification, and the final website response. The -v output can expose connection metadata and, depending on authentication settings, sensitive information; redact logs before sharing.
Only use https:// if the proxy itself supports TLS:
curl -v --proxy https://proxy.example.test:8443 \
  --proxy-cacert /path/to/approved-proxy-ca.pem \
  https://example.com/ -o /dev/null
The --proxy-cacert option sets a trusted CA bundle for the proxy connection. By contrast, --cacert configures destination-server certificate trust. Both certificate contexts are explained in cURL's SSL certificate documentation. Omit custom CA options if the certificates already chain to trusted roots.
Do not use -k, --insecure, or --proxy-insecure as a production fix. Those options disable important certificate checks and can hide interception or identity problems.
Python Requests supports HTTPS destinations through an HTTP proxy. Notice that the https dictionary key represents the destination scheme, while the value's http:// scheme describes the proxy connection:
import requests

proxies = {
    "https": "http://proxy.example.test:8080"
}

response = requests.get(
    "https://example.com/",
    proxies=proxies,
    timeout=(5, 20),
)
response.raise_for_status()
print(response.status_code)
Certificate verification is enabled by default. For an approved custom CA bundle, configure the trust store according to Requests' proxy and TLS documentation. Avoid verify=False: it suppresses certificate identity and trust checks, exposing requests to man-in-the-middle attacks.
Requests may also read proxy settings from environment variables. Explicitly check HTTPS_PROXY, HTTP_PROXY, and NO_PROXY if behavior differs between a laptop, container, and production server.
Debug in the order the connection is established:
http:// or https:// proxy scheme match the endpoint?For crawling and monitoring deployments, log these stages separately instead of recording everything as “proxy failed.” Segmented metrics reveal whether a change in target compatibility, authorization, or certificate trust is responsible. Consider the supported workloads described on the proxy use-cases landing page and validate target behavior using the compatible websites directory.
A normal, non-intercepting CONNECT proxy forwards encrypted TLS traffic without decrypting application content. An explicitly configured TLS-inspection proxy can decrypt it when the client trusts the inspection certificate authority.
CONNECT is the common method for HTTPS destinations through traditional HTTP forward proxies. Other proxy protocols and HTTP versions can have different mechanisms, but the goal remains carrying destination traffic through an intermediary.
The proxy may reject CONNECT, deny the target port, use the wrong endpoint protocol, or expose a destination TLS certificate issue. Compare the initial tunnel response with the later TLS result to locate the failure.
Yes. A TLS-enabled proxy endpoint has its own certificate, and a TLS-intercepting proxy may present a substituted destination certificate. Ordinary passthrough also exposes pre-existing destination certificate problems to the client.
No. Verify the proxy scheme, inspect the certificate issuer and hostname, and configure the correct trusted CA only when appropriate. Disabling verification removes protection against impostor endpoints.
Yes, Proxies That Work supports HTTP/HTTPS protocol support and IP authentication. Confirm the supplied proxy endpoint scheme before assuming TLS is available on the client-to-proxy connection.
Reliable HTTPS proxy configuration starts by separating the proxy connection, the CONNECT tunnel, and the destination TLS session. CONNECT creates the forwarding path; TLS protects the application traffic; certificates authenticate the relevant endpoint. Diagnose failures in that sequence, retain certificate verification, and choose proxy infrastructure that matches the transport and access-control requirements of the workload.
Jesse Lewis is a researcher and content contributor for ProxiesThatWork, covering compliance trends, data governance, and the evolving relationship between AI and proxy technologies. He focuses on helping businesses stay compliant while deploying efficient, scalable data-collection pipelines.